News & insights
Latest WordPress notes, plus longer pieces on development, consulting, APIs, and WooCommerce from this practice.
This WordPress blog is where I write up what I run into on real projects: security fixes for live sites, PHP and WordPress updates, performance and Core Web Vitals, WooCommerce, API integrations and technical architecture. Each article is meant to be practical, with steps you can follow on your own site.
Good places to start are the guide to the PHP2Shell security threats, the WooCommerce performance checklist and the WordPress Core Web Vitals guide. If you would rather have someone handle it for you, see my website security and maintenance service or the full list of WordPress services, or get in touch about your project.
Writing
Notes from delivery work
Theme builds, consulting, APIs, and WooCommerce — grouped by the work they cover.
Consulting, security, hosting
APIs and headless
WooCommerce
Latest
LiteLLM Supply Chain Attack: What Happened and What Python Teams Should Do
If your team uses Python for anything AI related, there is a good chance LiteLLM is somewhere in your stack. It is a popular gateway that lets one codebase talk to many model providers. On October 21, a poisoned release of it spent about two hours on PyPI and Docker registries. This post explains what…
Essential WordPress Project Brief Before First Call
Learn what to include in your WordPress project brief before the first call. Key details can streamline your engagement process for better outcomes.
Key Components of a Robust WordPress Production Stack
Explore the essential components of a WordPress production stack, including core, ACF, and API integrations, for optimal site performance. A practical A.
Forward Deployed Engagement: Understanding the Process
Explore the forward deployed engagement process for WordPress. Understand what to expect in each phase: discover, prototype, deploy, and support.
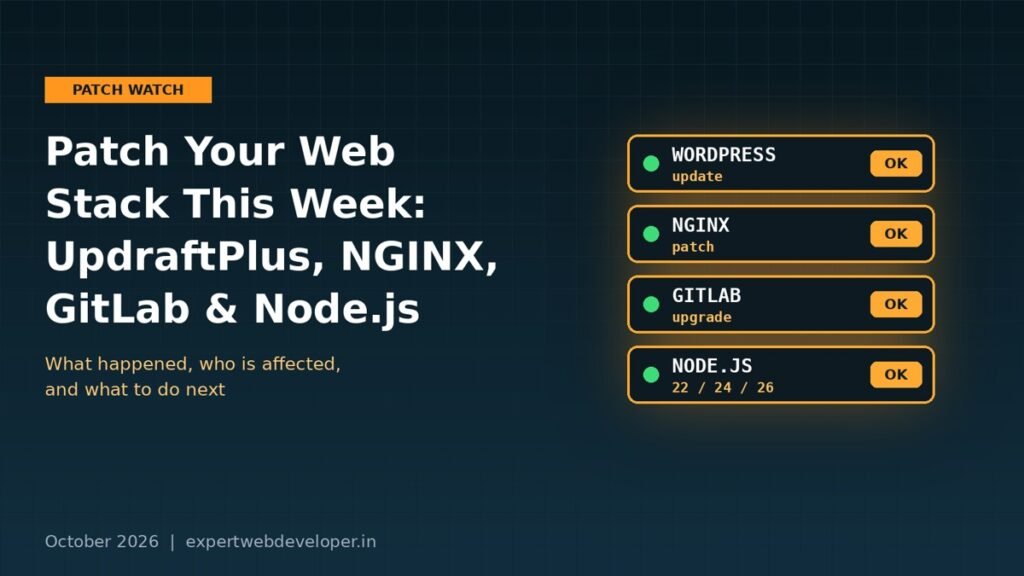
Web Stack Security Patches This Week: UpdraftPlus, NGINX, GitLab and Node.js
A plain-language roundup of this week’s web stack security patches: UpdraftPlus key theft, NGINX critical fixes, a GitLab CVSS 10.0 flaw and a Node.js Brotli bug, with what to do next.